Singapore will take steps towards establishing a national accreditation framework for cybersecurity professionals, with a voluntary pilot scheduled to begin in the second quarter of 2027. The initiative aims to establish consistent professional standards across the sector and help employers assess cybersecurity expertise across different roles and specialisations.
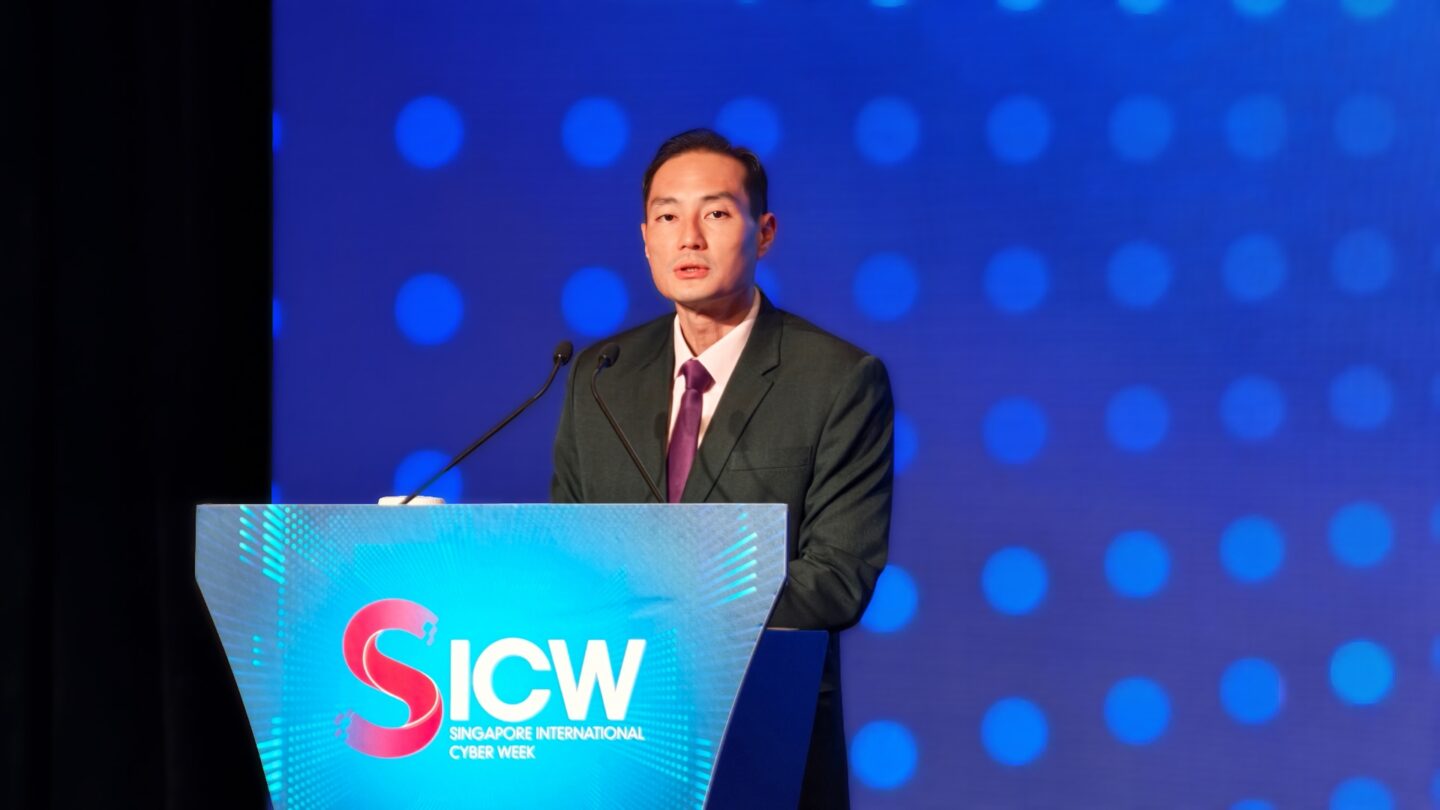
Announced by Senior Minister of State for Digital Development and Information Tan Kiat How at Singapore International Cyber Week 2026, the programme forms part of Singapore’s Cybersecurity Strategy 2026, which identifies workforce development as a national priority. The Cyber Security Agency of Singapore (CSA) will first develop national competency standards for different cybersecurity roles. These will underpin the Cybersecurity Professional Accreditation Framework, which will assess professional competence through qualifications, demonstrated capabilities, relevant experience and professional conduct.
Addressing gaps in cybersecurity skills assessment
The move comes amid rapid expansion in Singapore’s cybersecurity workforce, which has more than doubled over the past decade from 4,000 professionals in 2016 to more than 10,000 in 2025. With cyber threats becoming increasingly sophisticated, CSA is seeking a more consistent way to assess whether practitioners have the skills, experience and judgement required for their responsibilities.
A study commissioned by CSA and conducted by Ernst & Young across 2024 and 2025 highlighted clear challenges within the existing credentialing landscape. The wide range of cybersecurity certifications on the market can make it difficult for employers to evaluate professional competencies, while individuals often struggle to identify and maintain the skills needed for their roles and career progression. Ernst & Young found that although existing certifications remain valuable, they do not provide a comprehensive assessment covering technical knowledge, practical experience and professional ethics together. About 67% of stakeholders surveyed considered Singapore ready or somewhat ready to introduce a professional accreditation framework.
The proposed framework will complement existing industry qualifications and certifications by placing greater emphasis on demonstrated capabilities, relevant experience and professional conduct. This approach is intended to provide professionals with formal recognition of their expertise while giving employers a common basis for evaluating cybersecurity capabilities.
National competency standards to underpin accreditation
To build the foundation for accreditation, CSA is working with the Infocomm Media Development Authority (IMDA) and the Skills and Workforce Development Agency (SWDA) to establish a national cybersecurity competency framework covering different professional roles and proficiency levels. This will involve updating and aligning the cybersecurity track under the Skills Framework for Infocomm Technology (SFw for ICT) alongside CSA’s Operational Technology Cybersecurity Competency Framework (OTCCF). The resulting standards will define the knowledge, skills and abilities expected of cybersecurity professionals at different stages of their careers, with regular updates planned to account for changing industry requirements and emerging areas such as AI security.
Building on these competency standards, the accreditation framework will allow professionals to apply for professional titles aligned with their specialisations, evaluating applicants on relevant work experience, demonstrated competencies, qualifications, industry certifications and professional conduct. The pilot will initially involve professionals from selected government agencies and cybersecurity service providers. Focusing on specialisations that include security operations and Vulnerability Assessment & Penetration Testing (VAPT), participation will remain voluntary, with application fees waived throughout the pilot.
Three bodies to oversee professional accreditation
CSA will establish three bodies by the end of 2026 to administer accreditation, oversee professional standards and assess applicants. The Cyber Security Professional Office (CSPO), to be established in collaboration with the Association of Information Security Professionals (AiSP), will manage the accreditation process, including assessments, appeals, renewals and maintaining a public register of accredited professionals. Strategic oversight will be provided by a Cyber Security Professional Panel (CSPP), comprising senior representatives from government, industry and academia, to guide the development of professional standards and approve the award of professional titles to individuals.
Accreditation Committees comprising technical experts across cybersecurity specialisations will develop and periodically review professional standards and assessment criteria. They will also participate in portfolio reviews and interviews for applicants seeking professional titles, helping ensure that accreditation requirements remain aligned with evolving cybersecurity practices and technologies. Further information on accreditation standards, eligibility requirements, assessment procedures and applications will be available from March 2027, ahead of the voluntary pilot.